Runtime control for AI agents, wherever they work.
Tego governs what an agent can do the moment it acts, session by session, across the industries and teams where the wrong action costs real money, real trust, or real regulatory exposure.
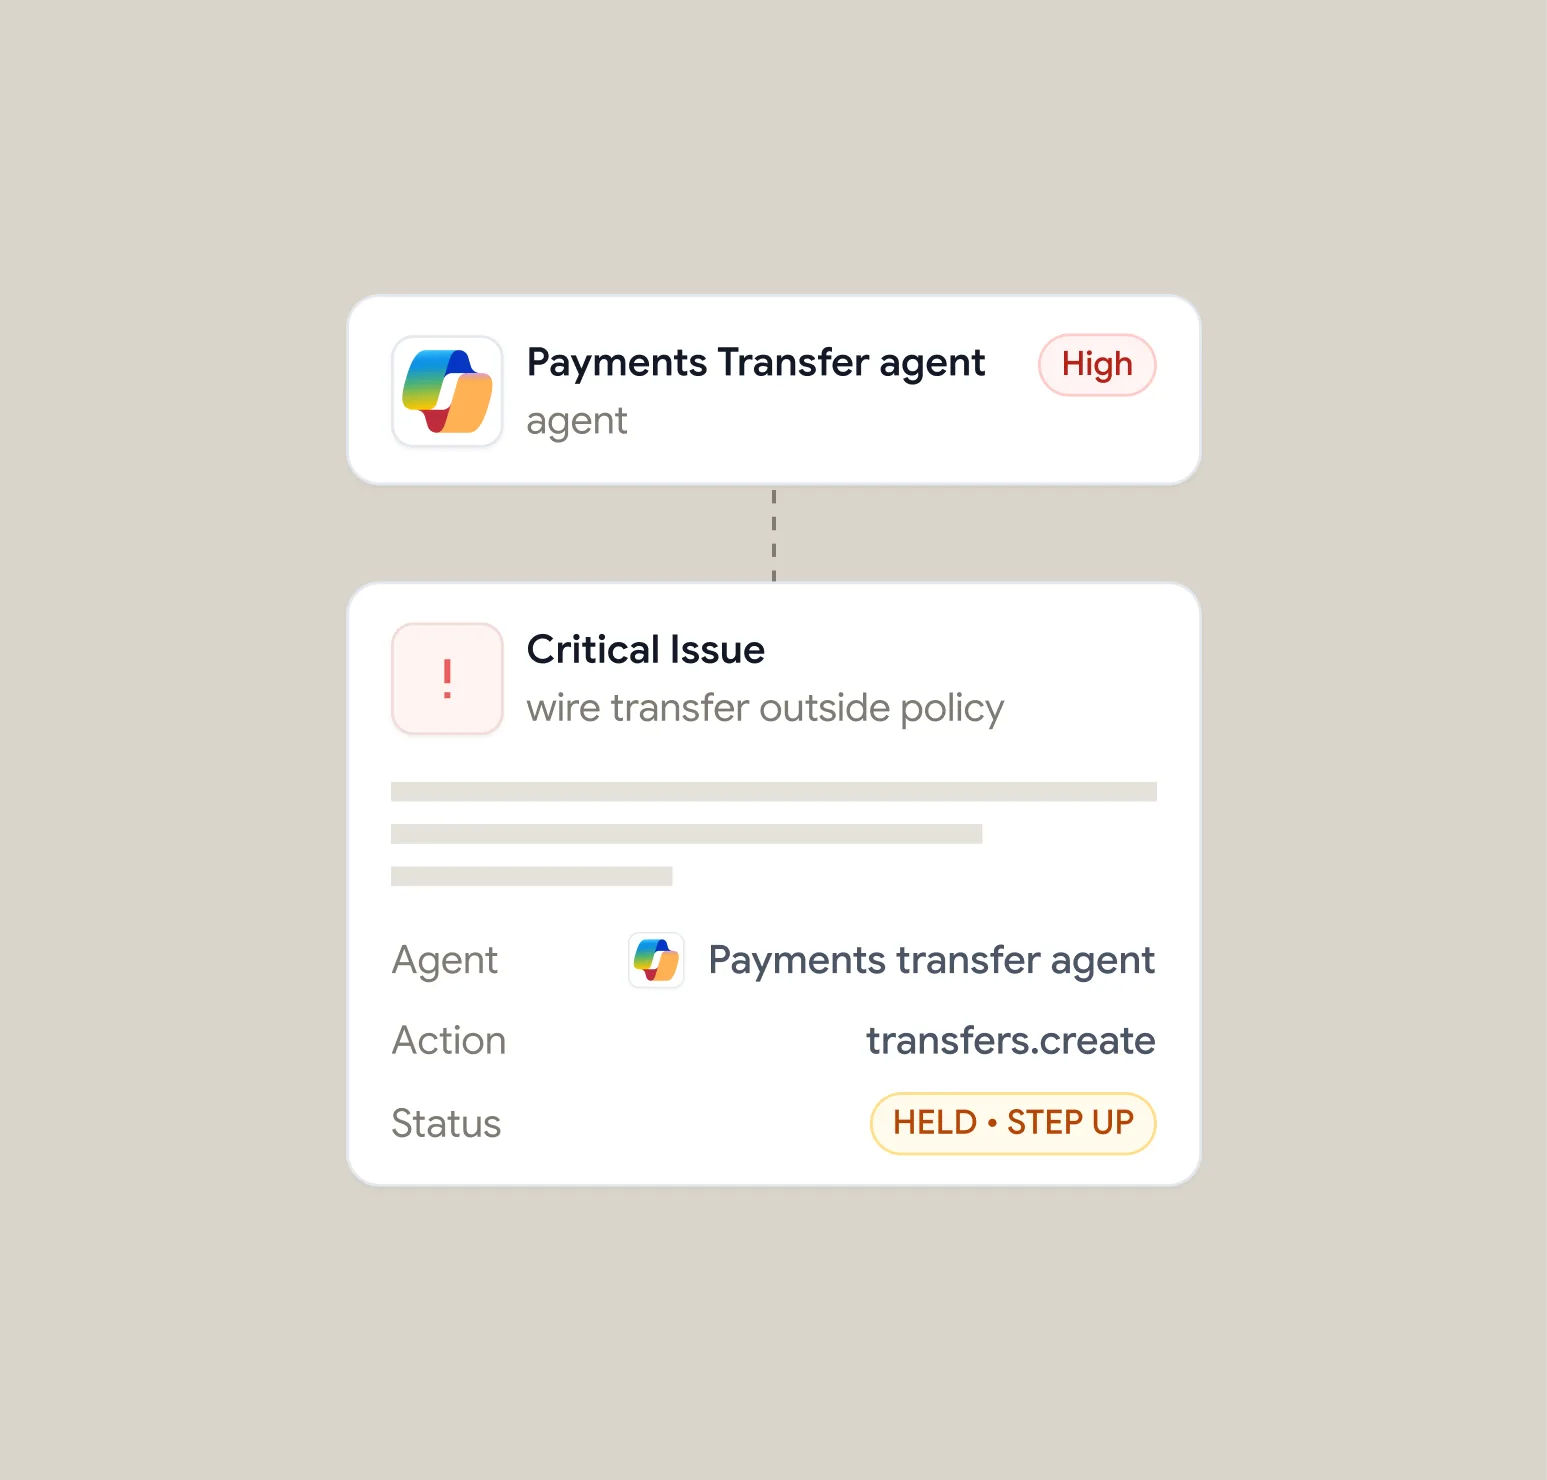
Agents reconcile transactions, pull records, and trigger payments. The risk is what they execute, not what they say.
- SOX, PCI, GLBA evidence at the session level
- Step-up enforcement before money movement
- Velocity caps on runaway batch activity
Agents move real money instantly, leak contracts across the supply chain, trigger each other with authority no one granted, and can disrupt physical operations.
Scores every session for privilege, data sensitivity, reversibility, and velocity Steps up auth before money moves Blocks irreversible actions outside policy PII and PCI DLP run out of the box
Stop a prompt from becoming a wire.
One over-scoped session turns a prompt into an irreversible transfer, or a full book of customer records into an exposure. Tego scores every session for privilege, sensitivity, reversibility and velocity, then steps up or blocks before the money moves.
Agents summarize charts, query EHRs, and submit claims. IAM sees a
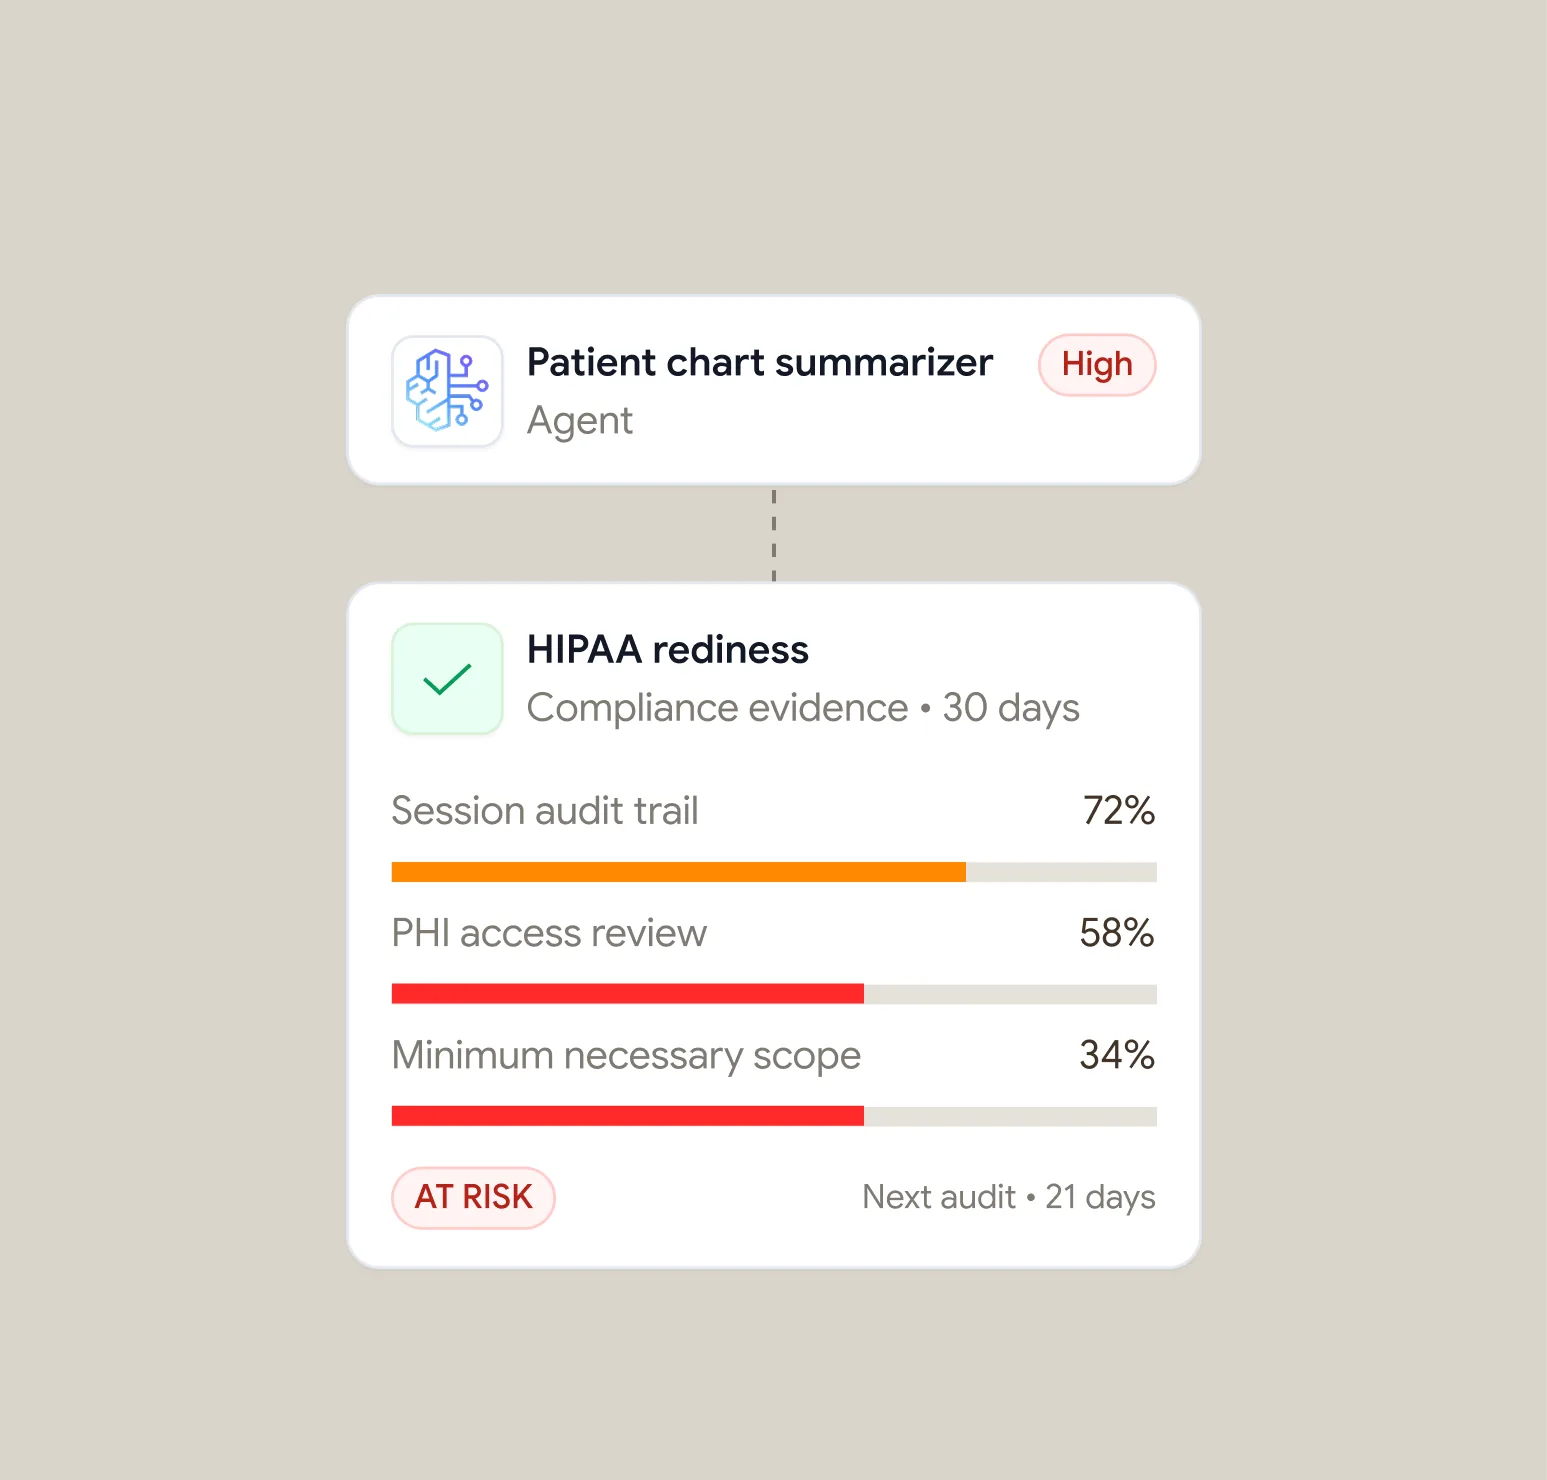
- HIPAA-grade session audit
- Least-privilege scope on every PHI session
- Reversibility gates on clinical and billing writes
Over-broad sessions read records they never needed — HIPAA breach on a log line. Agents write claims irreversibly, crossing trust boundaries no one authorized.
Enforces least privilege per session Gates record writes on reversibility PHI DLP runs out of the box Audit reaches the session, not just the service account
Govern what the agent touches, not just what it types.
An over-broad session reads charts it never needed, and a record write or a filed claim is hard to walk back. Tego scopes every session to least privilege, gates writes on reversibility, and audits down to the session rather than the service account.
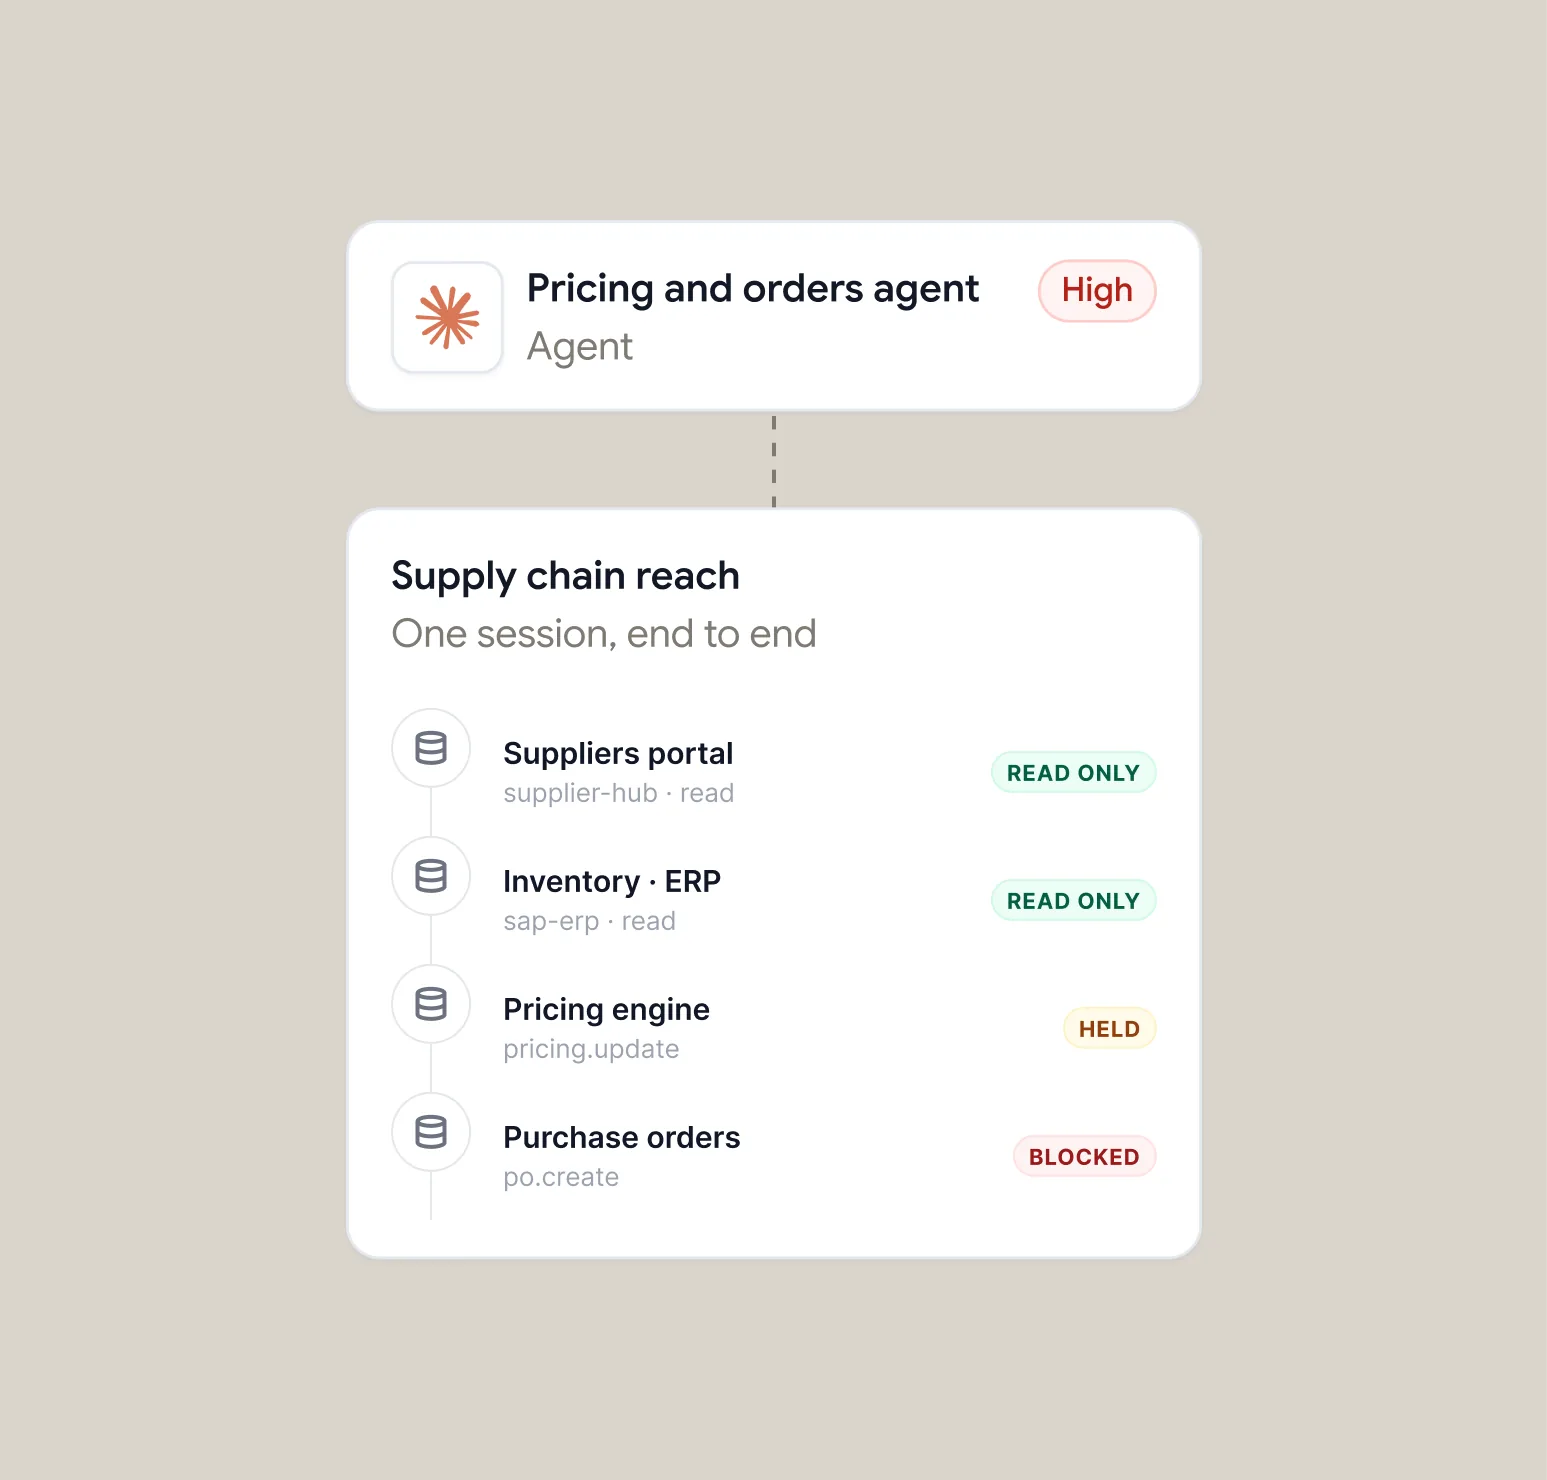
Agents manage pricing, inventory, suppliers, and fulfillment. They act fast, atscale, across commerce and supply systems.
- Velocity and step-up control on pricing
- Reversibility gates on orders and inventory writes
- Session-level audit across the supply chain
Agents move real money instantly, leak contracts across the supply chain, trigger each other with authority no one granted, and can disrupt physical operations.
Caps velocity on high-value actions and steps up before they execute Gates orders and pricing changes on reversibility Protects contract and forecast data with DLP
Velocity is the threat. Control it at the session.
A pricing change or a purchase order moves real money in seconds, and one session can reach across the supply chain into contracts and forecasts. Tego caps velocity, gates orders and pricing on reversibility, and keeps that data behind DLP.
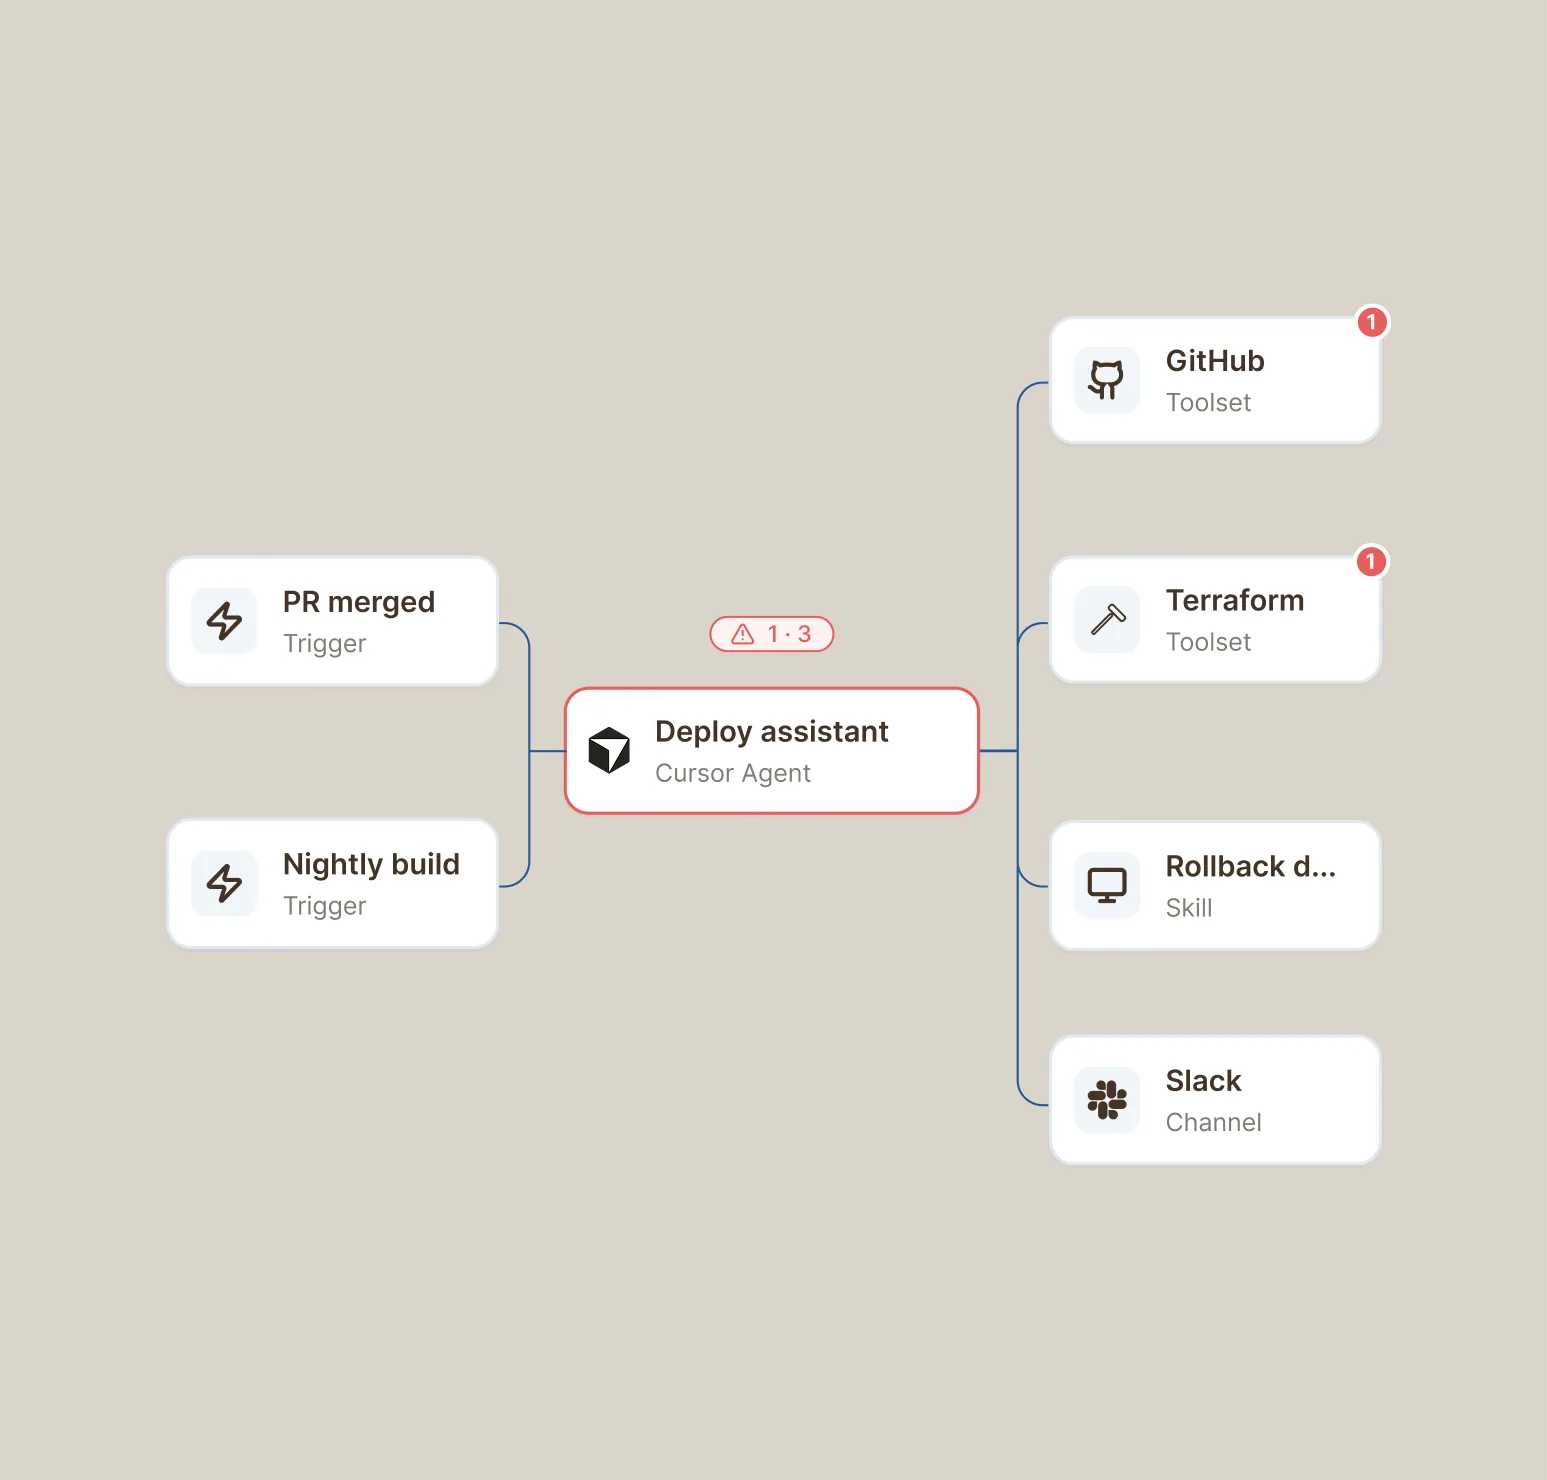
AI agents now work in every department, replacing and amplifyingemployees, with the same reach into company systems.
- Inventory and control across MCP and all connectors
- Cedar-enforced least privilege per session
- Reversibility gates on deploys and prod writes
Agents hold employee access without judgment. Every connector adds untracked reach — prompts become production changes, customer records leak silently.
Governs every connector a session reaches: MCP servers and beyond Cedar policy engine scopes authority per session Reversibility gates protect production Runs OpenTelemetry native
Your agents have employee access. Not employee judgment.
Every MCP server and connector adds reach nobody tracked, and a coding agent with deploy access turns a prompt into a production change. Tego inventories what each session can touch, scopes its authority with Cedar, and gates anything that cannot be undone.
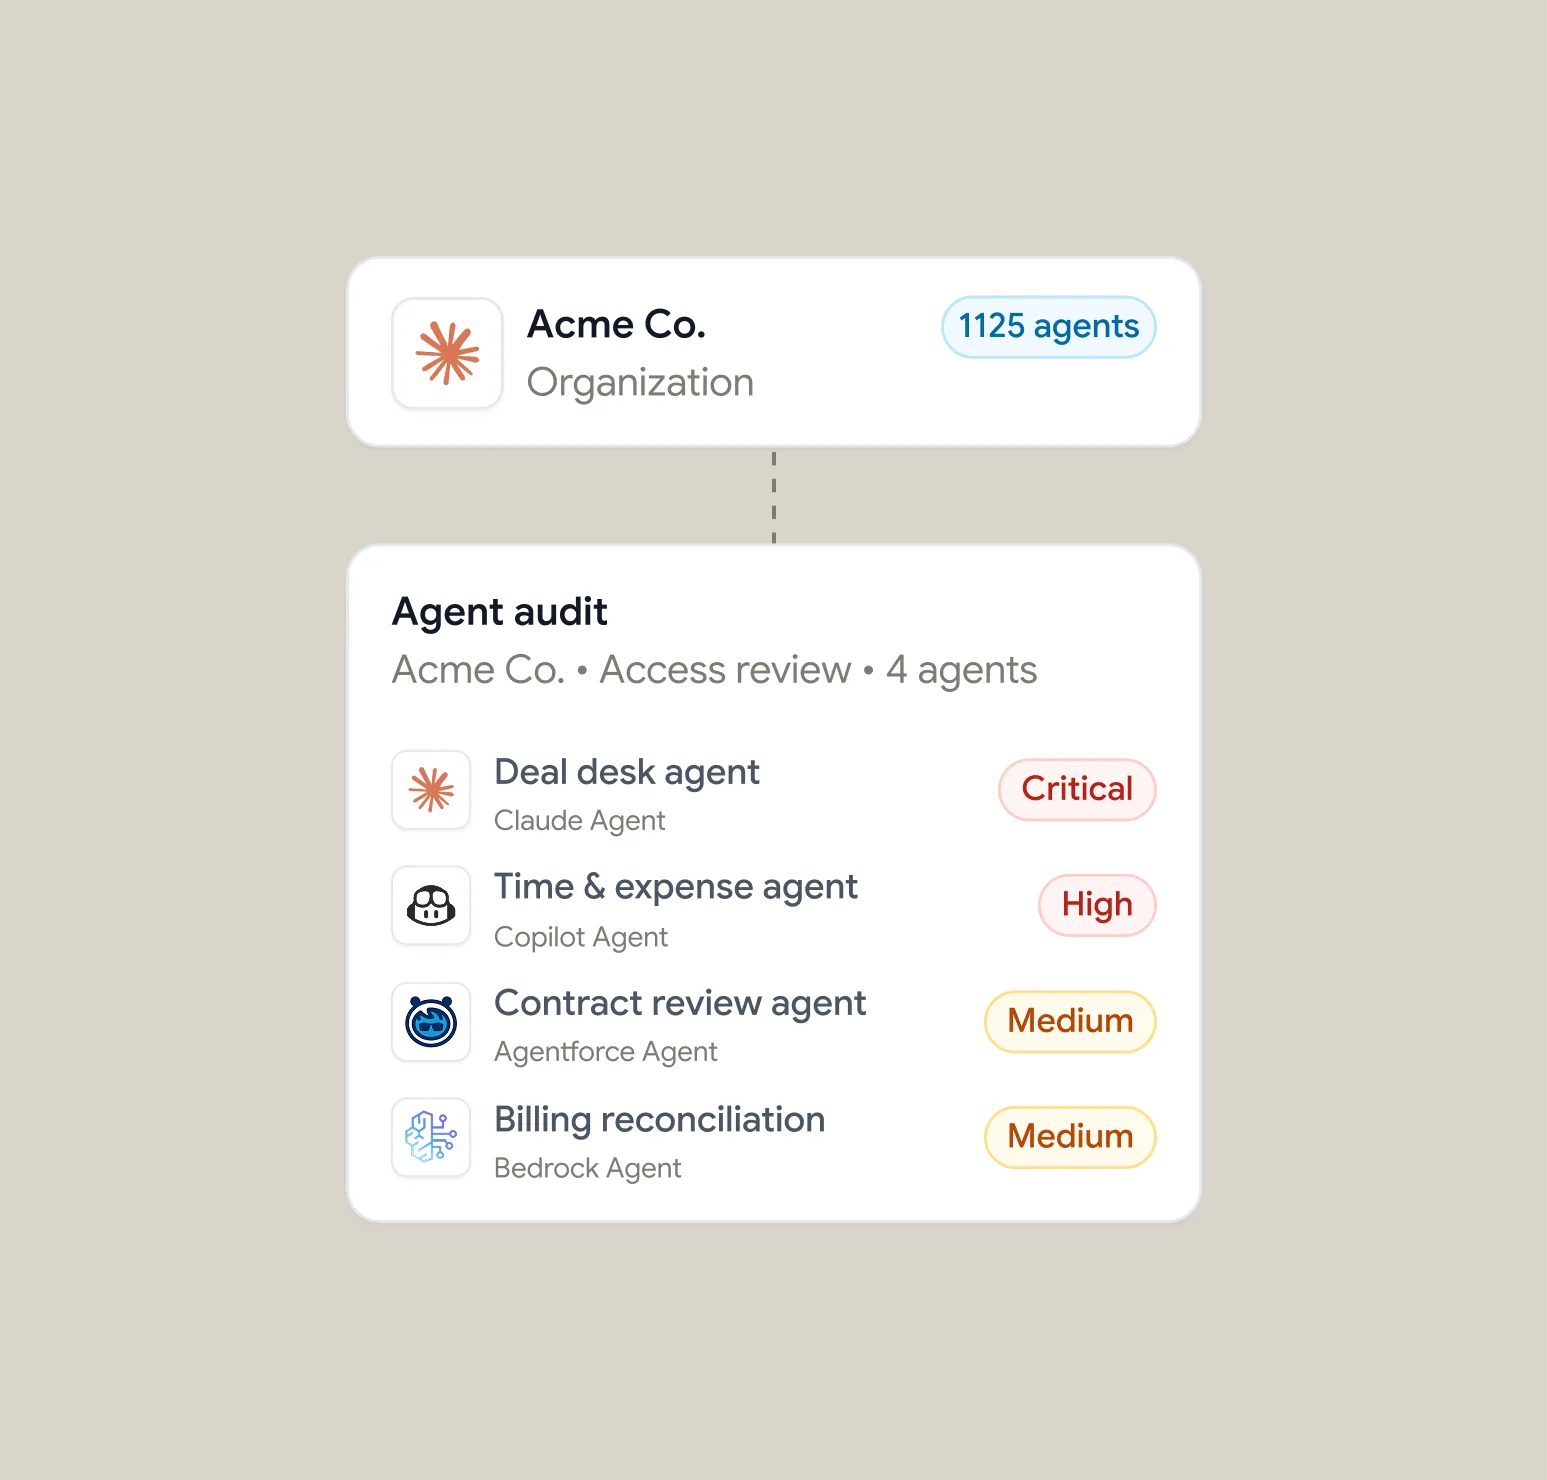
For agencies, consultancies, and managed security and IT providers, agentsrun on behalf of many clients at once.
- Tenant isolation enforced per session
- Per-engagement least privilege across clients
- Audit you can deliver to clients as proof
One agent, many clients — mixing A into B ends a contract. Access accumulates across engagements, blast radius lands on your customer. Controlling agents is a sales requirement.
Enforces hard tenant isolation at the session level Scopes least privilege per engagement Produces client-facing session audit you can hand over as evidence DLP keeps each client's data in its lane
Your agents run inside their systems. One mistake costs you the client.
One agent serves many clients, and a session that mixes one into another ends a contract. Tego enforces tenant isolation and per-engagement scope at the session level, and produces an audit you can hand to the client as evidence.
Every department runs agents now.
Tego governs each one.
The agents running across your org are different by team, different tools, different data, different risks. Here's what that looks like in practice.

Coding agents write production code, review PRs, debug errors, and deploy changes, with direct access to your codebase, CI/CD pipeline, and environment secrets.
Sales agents prospect, update CRM records, draft outreach, and trigger sequences, often with access to contact data, deal history, and communication tools.
Marketing agents generate content, run campaign logic, analyze performance data, and publish across channels, often acting autonomously at scale.
Support agents handle tickets, answer questions, process refunds, and access account history, interacting with customers directly under your brand.
Finance agents reconcile transactions, generate reports, flag anomalies, and in some cases trigger payments, with access to financial systems and sensitive records.
Legal agents review contracts, flag risk clauses, redline documents, and summarize case materials, touching some of the most confidential content in the org.
